
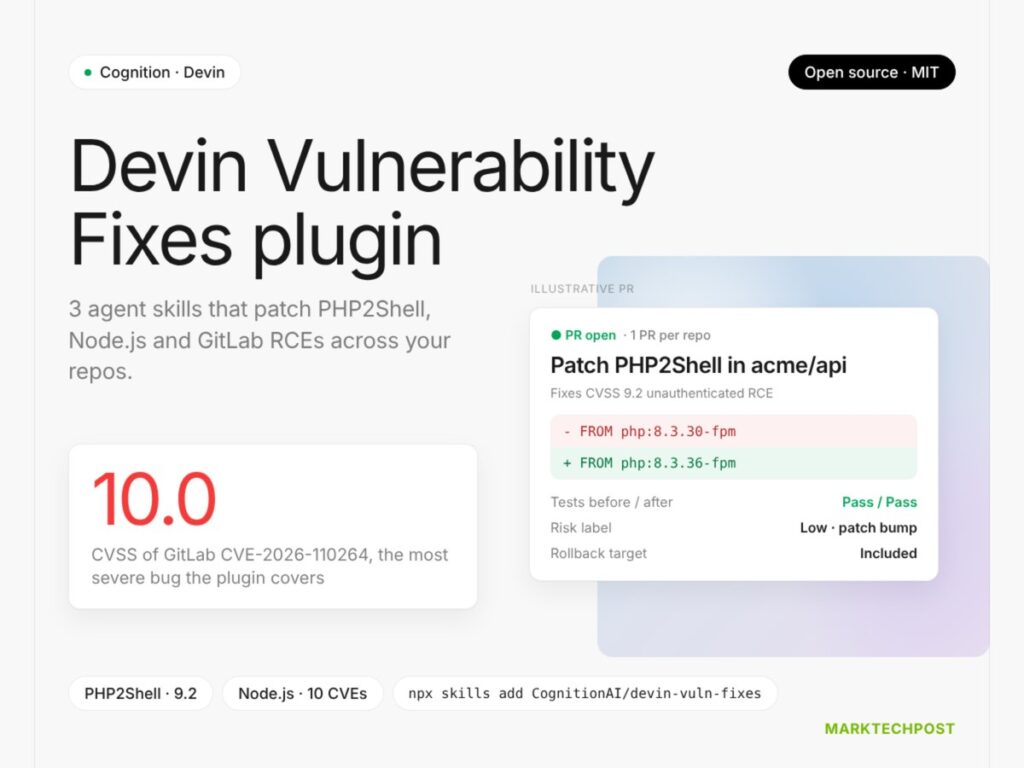
Cognition has open-sourced a plugin that turns its Devin coding agent into a rapid-response patch crew. The Devin Vulnerability Fixes plugin, released under the MIT license, targets three critical remote-code-execution advisories from the past week: a PHP flaw dubbed PHP2Shell, the Node.js security release of October 21, 2026, and a self-managed GitLab bug rated CVSS 10.0, the maximum severity score.
The plugin ships as three agent skills, one per flaw, and it works in Devin as well as in any coding agent that reads SKILL.md files, including Claude Code, Codex, Cursor, GitHub Copilot, and Windsurf. Installation is a single command, and it requires Node.js 22.20 or later.
Each skill follows the same careful workflow. It starts with a read-only inventory of affected repositories, pauses at an approval gate, then patches to verified fixed versions, runs tests before and after, and opens one pull request per repository. Managed runtimes and vendor appliances are flagged rather than patched, since those fixes must come from the provider.
The release is notable because it packages the exact remediation workflow Cognition used internally, and gives it away. For teams drowning in patch backlogs, an agent that can triage and fix a critical flaw across many repos at once is a practical use of AI coding tools. Readers can compare the agents involved in our directory: Devin, Cursor, and GitHub Copilot.
Source: MarkTechPost, Cognition


